
pyLoad's Session Not Invalidated After Permission Changes
Summary
The pyload application does not properly invalidate or modify sessions upon changes made to a user's permissions.
Details
Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the pyload application, as a user with a valid session can still perform the actions.
PoC
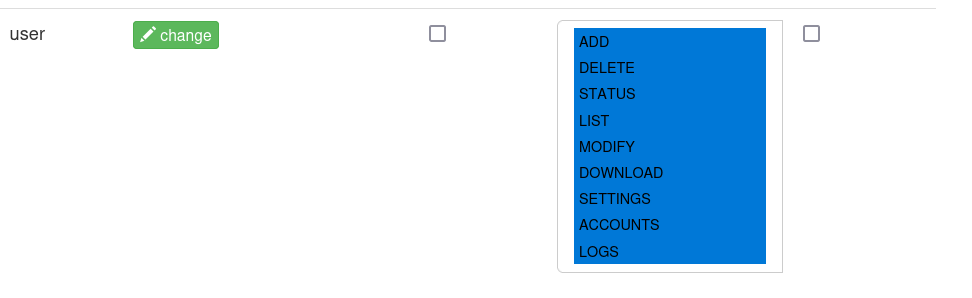
Take a user with all the permissions, as shown below.
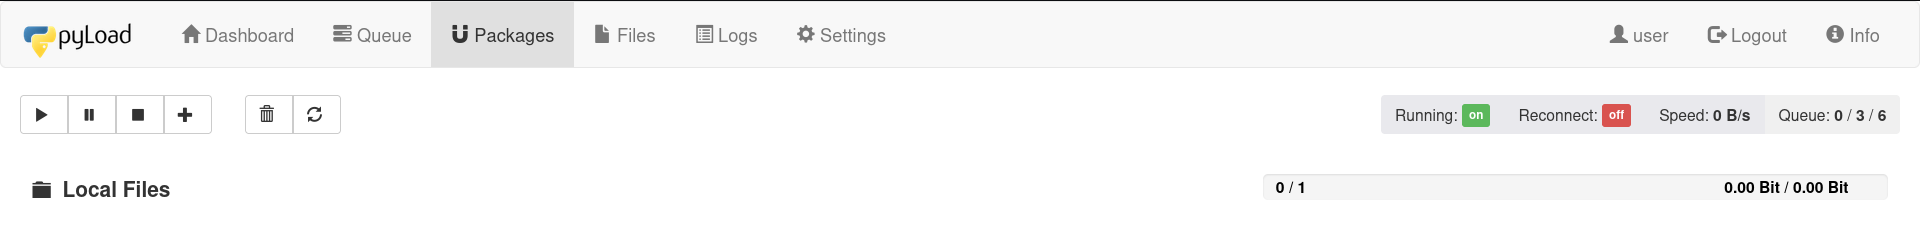
We now log in as this user.
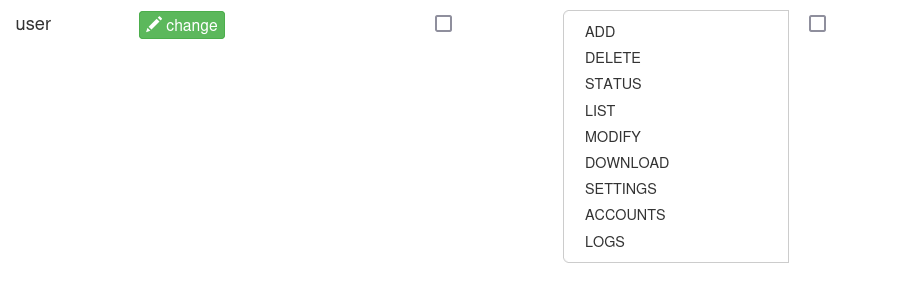
Let us now take away all the permissions.
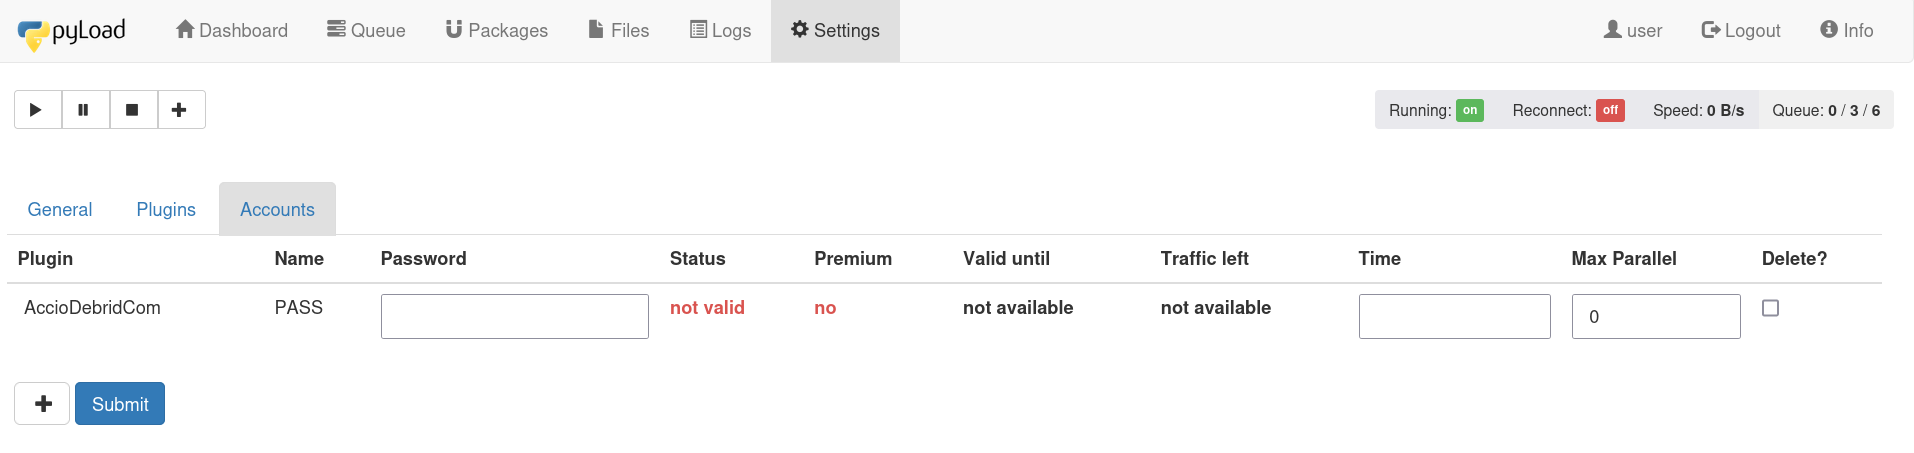
The logged in session can still be used to access everything in the application.
Impact
Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
Affected software
Click a technology to see all vulnerabilities affecting it.
| Platform | Package | Vulnerable versions | Fixed in |
|---|---|---|---|
| Python (PyPI) | pyload-ng | <= 0.5.0b3.dev97 | no fix |
References
- CVSS vector
CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N/E:P- Weakness (CWE)
CWE-613- Platform
- Python (PyPI)
- Package
pyload-ng- Disclosed
- 14.04.2026
- Updated
- 11.10.2026 12:19
Sources and licenses
OSV / GitHub Advisory Database - GHSA-fj52-5g4h-gmq8 - CC BY 4.0
Vulnerability history: pyload-ng
All published vulnerabilities of this package (Python (PyPI)), newest first. Shows whether this is a one-off slip or a package that needs watching.
- Total entries
- 58
- First → latest
- 01.2023 10.2026
- Without a fix
- 24
- Exploited in attacks
- 0
Severity breakdown
- Critical 9
- High 23
- Medium 25
- Low 1
Disclosures per year
- 2023: 9
- 2024: 8
- 2025: 8
- 2026: 33
-
pyLoad's Session Not Invalidated After Permission Changes this entry
Know which vulnerabilities affect your application
With the DockRay integration and software inventory enabled, DockRay checks reported component versions against known vulnerabilities and notifies you about confirmed matches. Coverage depends on the supported technology and available advisory data.