
pyLoad's Session Not Invalidated After Permission Changes
Summary
The pyload application does not properly invalidate or modify sessions upon changes made to a user's permissions.
Details
Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the pyload application, as a user with a valid session can still perform the actions.
PoC
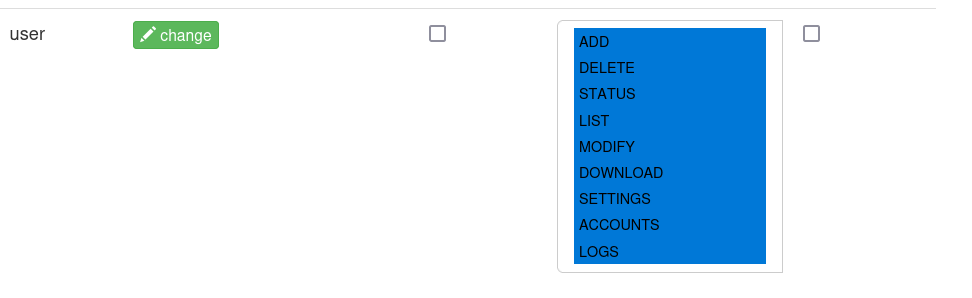
Take a user with all the permissions, as shown below.
We now log in as this user.
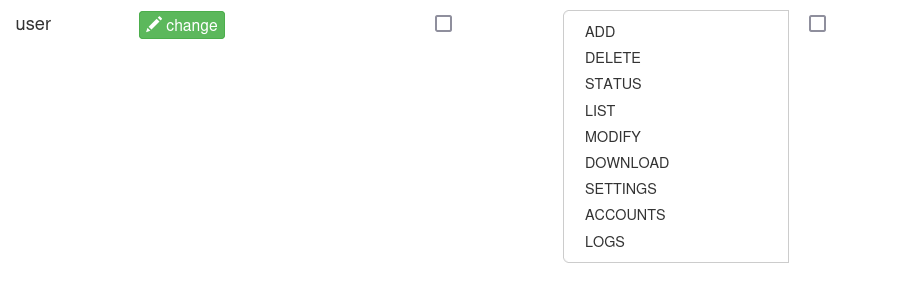
Let us now take away all the permissions.
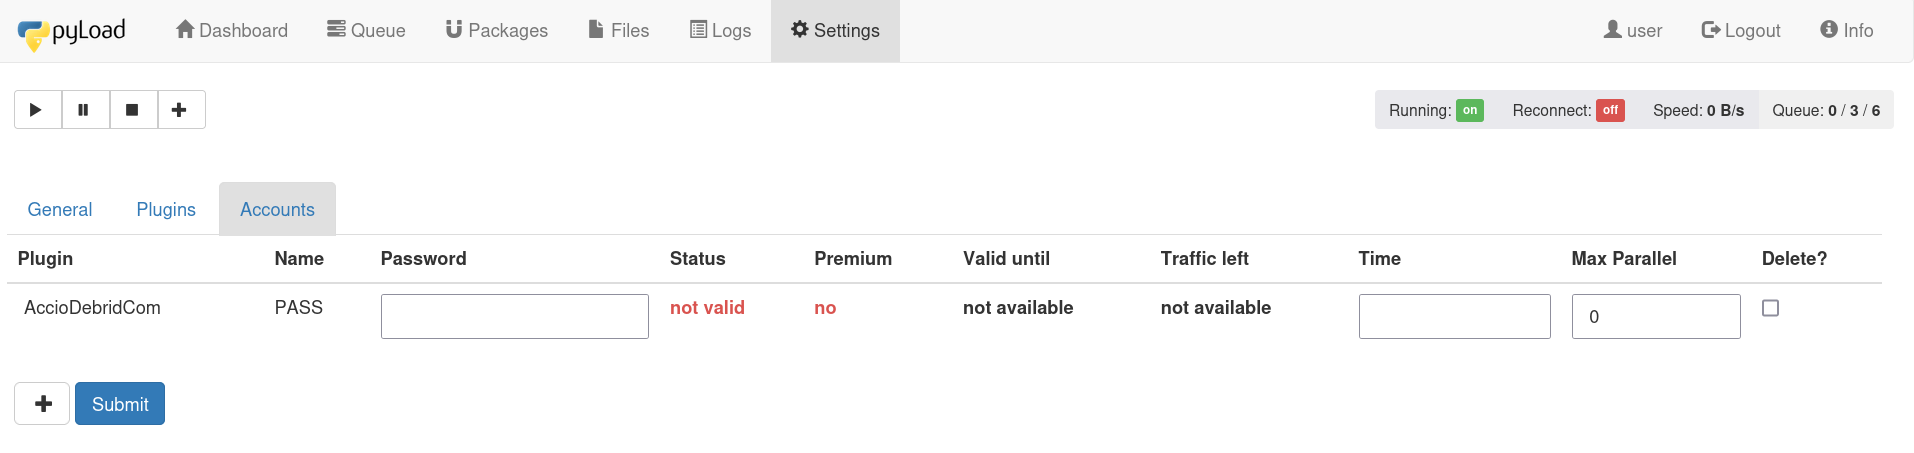
The logged in session can still be used to access everything in the application.
Impact
Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
Betroffene Software
Klicken Sie auf eine Technologie, um alle zugehörigen Schwachstellen anzuzeigen.
| Plattform | Paket | Anfällige Versionen | Behoben in |
|---|---|---|---|
| Python (PyPI) | pyload-ng | <= 0.5.0b3.dev97 | keine Korrektur |
Verweise
- CVSS-Vektor
CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N/E:P- Schwäche (CWE)
CWE-613- Plattform
- Python (PyPI)
- Paket
pyload-ng- Veröffentlicht
- 14.04.2026
- Aktualisiert
- 11.10.2026 12:19
Quellen und Lizenzen
OSV / GitHub Advisory Database - GHSA-fj52-5g4h-gmq8 - CC BY 4.0
Schwachstellenhistorie: pyload-ng
Alle veröffentlichten Schwachstellen dieses Pakets (Python (PyPI)), neueste zuerst. Zeigt, ob es ein einmaliger Ausrutscher ist oder ein Paket, das man im Auge behalten muss.
- Einträge insgesamt
- 58
- Erste → letzte
- 01.2023 10.2026
- Ohne Fix
- 24
- In Angriffen ausgenutzt
- 0
Verteilung nach Schweregrad
- Kritisch 9
- Hoch 23
- Mittel 25
- Niedrig 1
Veröffentlichungen pro Jahr
- 2023: 9
- 2024: 8
- 2025: 8
- 2026: 33
-
pyLoad's Session Not Invalidated After Permission Changes dieser Eintrag
Erkennen Sie Schwachstellen in Ihrer Anwendung
Mit der DockRay-Integration und aktivierter Softwareinventarisierung prüft DockRay gemeldete Komponentenversionen auf bekannte Schwachstellen und benachrichtigt Sie über bestätigte Treffer. Die Abdeckung hängt von der unterstützten Technologie und den verfügbaren Meldungen ab.