
Attribute Injection leading to XSS(Cross-Site-Scripting)
Summary
Google Analytics element Attribute Injection leading to XSS
Details
Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks.
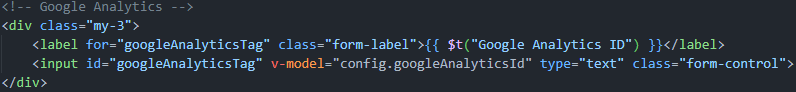
PoC
- Run the latest version of the louislam/uptime-kuma container and initialize the account password.
- Create a new status page.
- Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive):
123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x- Click Save and return to the interface. XSS occurs.
screenshots:


Affected software
Click a technology to see all vulnerabilities affecting it.
| Platform | Package | Vulnerable versions | Fixed in |
|---|---|---|---|
| npm package | uptime-kuma | >= 1.20.0, < 1.23.7 | 1.23.7 |
References
- CVSS vector
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N- Weakness (CWE)
CWE-79- Platform
- npm
- Package
uptime-kuma- Disclosed
- 24.11.2023
- Updated
- 11.10.2026 10:22
Sources and licenses
OSV / GitHub Advisory Database - GHSA-v4v2-8h88-65qj - CC BY 4.0
Vulnerability history: uptime-kuma
All published vulnerabilities of this package (npm package), newest first. Shows whether this is a one-off slip or a package that needs watching.
- Total entries
- 11
- First → latest
- 10.2023 03.2026
- Without a fix
- 1
- Exploited in attacks
- 0
Severity breakdown
- High 2
- Medium 8
- Low 1
Disclosures per year
- 2023: 4
- 2024: 4
- 2025: 2
- 2026: 1
-
Attribute Injection leading to XSS(Cross-Site-Scripting) this entry
Know which vulnerabilities affect your application
With the DockRay integration and software inventory enabled, DockRay checks reported component versions against known vulnerabilities and notifies you about confirmed matches. Coverage depends on the supported technology and available advisory data.