
Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution
Summary
A vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double file:// scheme (e.g., file://file:////). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads.
Note that this will only work if you have an authenticated administrator account with allowAdminChanges enabled.
https://craftcms.com/knowledge-base/securing-craft#set-allowAdminChanges-to-false-in-production
Details
The issue lies in line 57 of cms/src/helpers/FileHelper.php, it only removes file:// on the most left. It is trivial to bypass this sanitization by adding 2 file://, e.g. file://file:////.
    public static function normalizePath($path, $ds = DIRECTORY_SEPARATOR): string
    {
        // Remove any file protocol wrappers
        $path = StringHelper::removeLeft($path, 'file://');

        // Is this a UNC network share path?
        $isUnc = (str_starts_with($path, '//') || str_starts_with($path, '\\\\'));

        // Normalize the path
        $path = parent::normalizePath($path, $ds);

        // If it is UNC, add those slashes back in front
        if ($isUnc) {
            $path = $ds . $ds . ltrim($path, $ds);
        }

        return $path;
    }
PoC
- Sign in with an admin account and navigate to
Settings → Assets, then create a new volume. - n the Asset Filesystem section, create a new file system and set the Base Path to
file://file:////vendor. Without the prefix, the selection fails.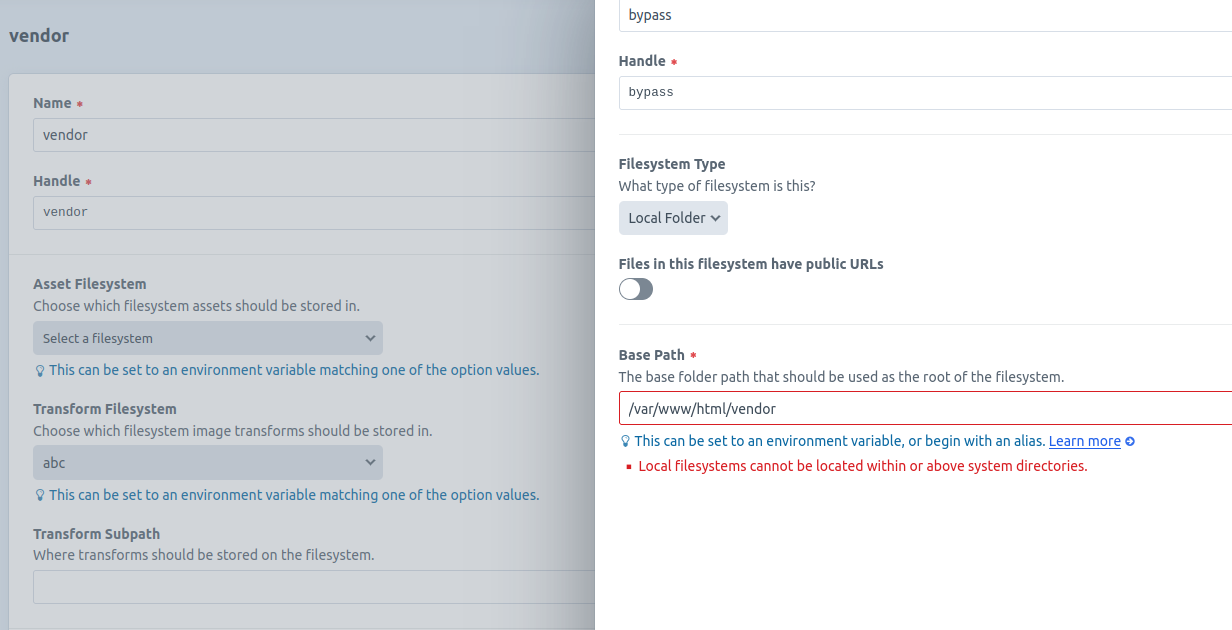 With the double
file://prefix, the selection succeeds.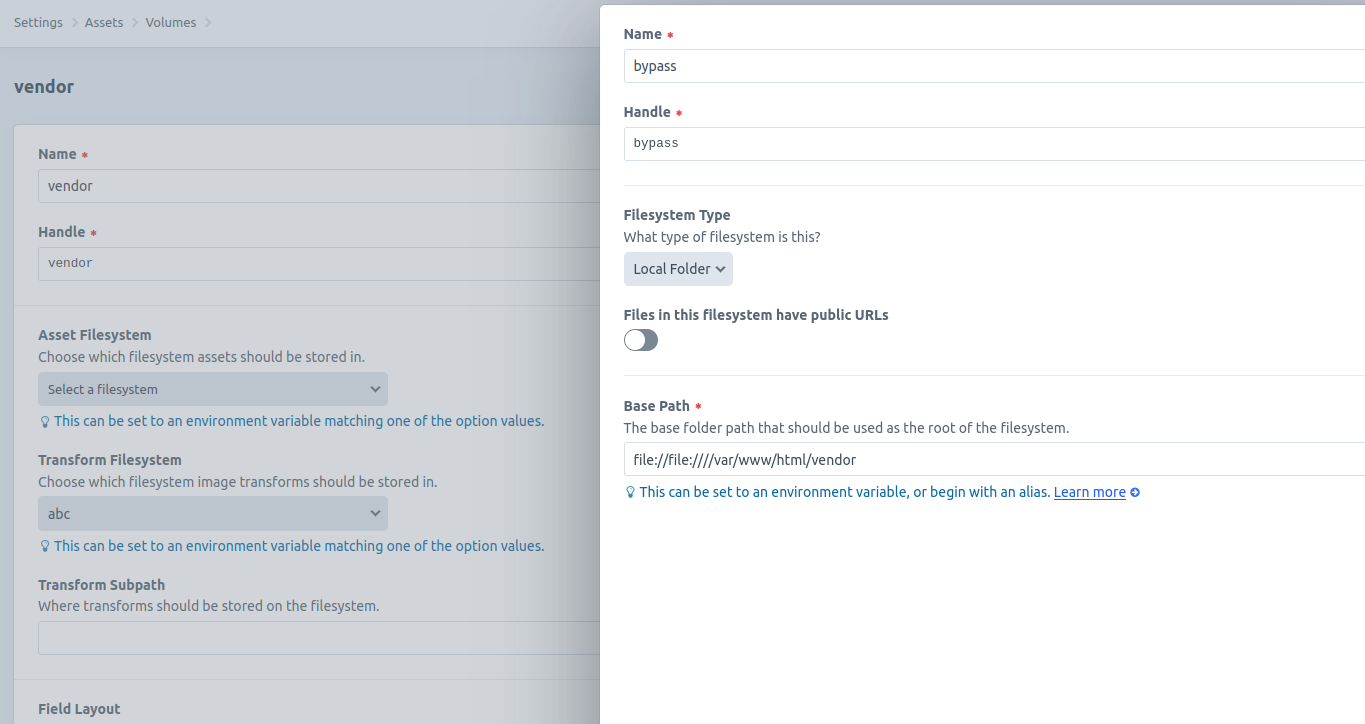
- Access Assets from the left navigation bar, then upload a file into this volume.
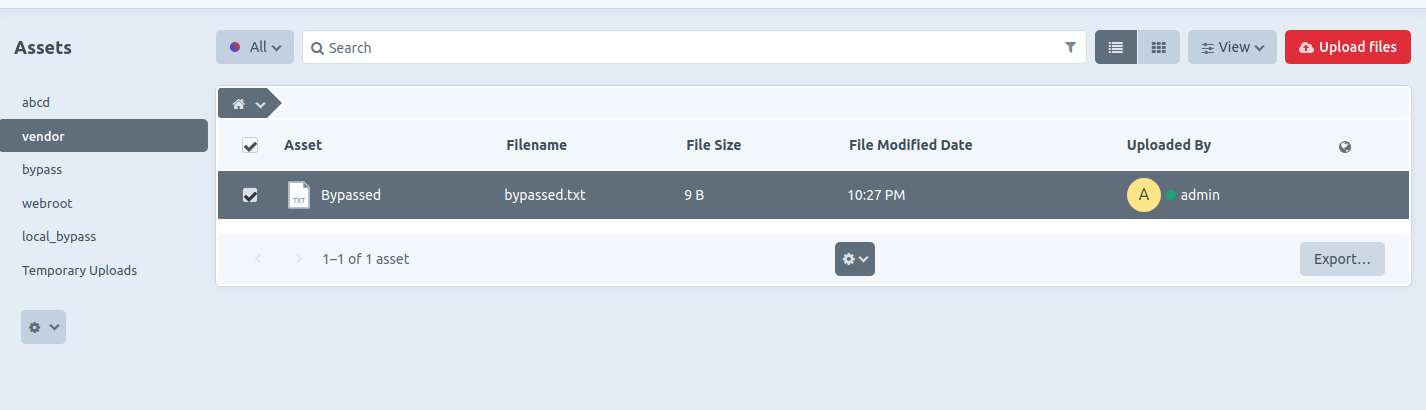
- The file is successfully uploaded and stored in the sensitive folder specified (e.g.,
/vendor).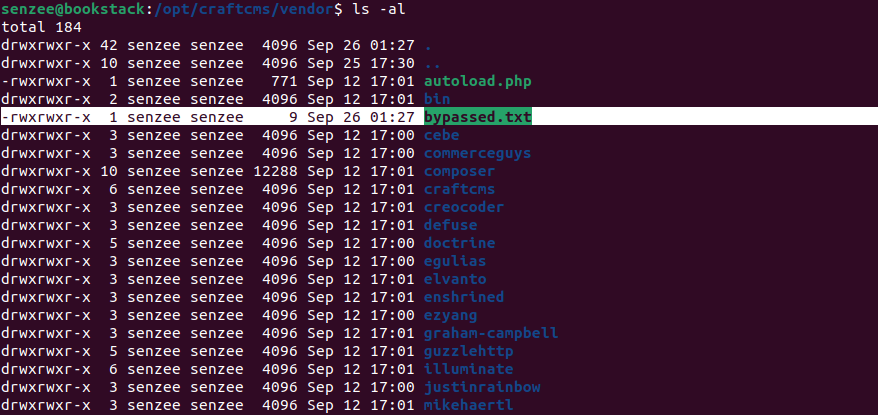
- SSTI payloads can be uploaded to
/templatesfolder, though full code execution was not achieved during testing, some payloads were still successful, leading to sensitive information disclosure, among other potential impacts.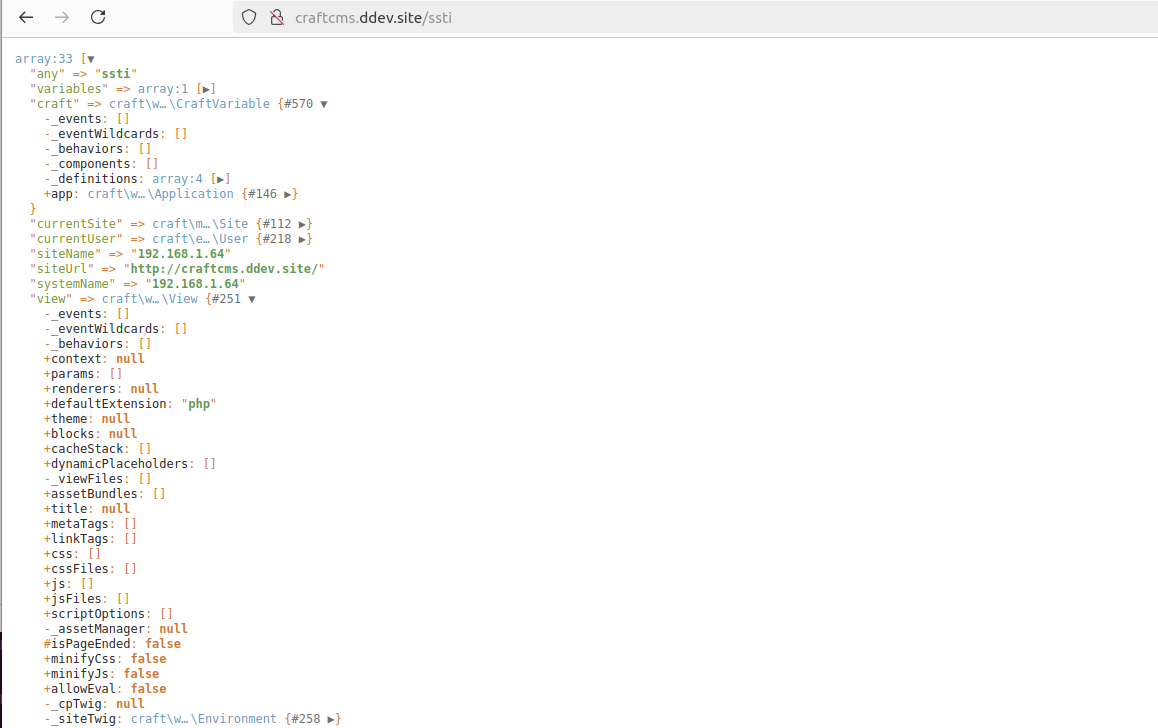
Impact
Attackers who compromise an admin account(The admin user is not equal to the server owner) can exploit this flaw to assign sensitive folders as the base path of the filesystem. For instance, if the path /templates is specified (e.g., file://file:////var/www/html/templates), the attacker could upload SSTI payloads. While CraftCMS includes strict SSTI input sanitization, RCE may still be possible if the attacker can craft a valid payload, as seen in similar vulnerabilities (e.g., GHSA-44wr-rmwq-3phw).
Additionally, attackers can upload tampered files to overwrite critical web application files. By enabling public URLs for files in the specified filesystem, they can also retrieve sensitive files (e.g., configuration files from the local file system).
Although the vulnerability is exploitable only in the authenticated users, configuration with ALLOW_ADMIN_CHANGES=true, there is still a potential security threat.
Software afectado
Haz clic en una tecnología para ver todas sus vulnerabilidades.
| Plataforma | Paquete | Versiones vulnerables | Corregida en |
|---|---|---|---|
| Paquete de Composer | craftcms/cms | >= 5.0.0-RC1, < 5.4.6, >= 4.0.0-RC1, < 4.12.5 | 5.4.6, 4.12.5 |
Referencias
- Vector CVSS
CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H- Debilidad (CWE)
CWE-22- Plataforma
- Composer
- Paquete
craftcms/cms- Publicada
- 13.11.2024
- Actualizado
- 11.10.2026 10:22
Fuentes y licencias
OSV / GitHub Advisory Database - GHSA-jrh5-vhr9-qh7q - CC BY 4.0
Historial de vulnerabilidades: craftcms/cms
Todas las vulnerabilidades publicadas de este paquete (Paquete de Composer), de la más reciente a la más antigua. Muestra si es un fallo aislado o un paquete que hay que vigilar.
- Entradas en total
- 127
- Primera → última
- 07.2021 08.2026
- Sin corrección
- 6
- Explotada en ataques
- 4
Distribución por gravedad
- Crítica 9
- Alta 41
- Media 65
- Baja 12
Divulgaciones por año
- 2021: 3
- 2022: 22
- 2023: 13
- 2024: 9
- 2025: 6
- 2026: 74
-
Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution esta entrada
Identifica las vulnerabilidades de tu aplicación
Con la integración de DockRay y el inventario de software activado, DockRay compara las versiones notificadas de los componentes con las vulnerabilidades conocidas y avisa de las coincidencias confirmadas. La cobertura depende de la tecnología compatible y de los avisos disponibles.